A dormant flaw in the XRP Ledger’s payment engine has raised fresh questions about how blockchain systems enforce their most fundamental economic rules.
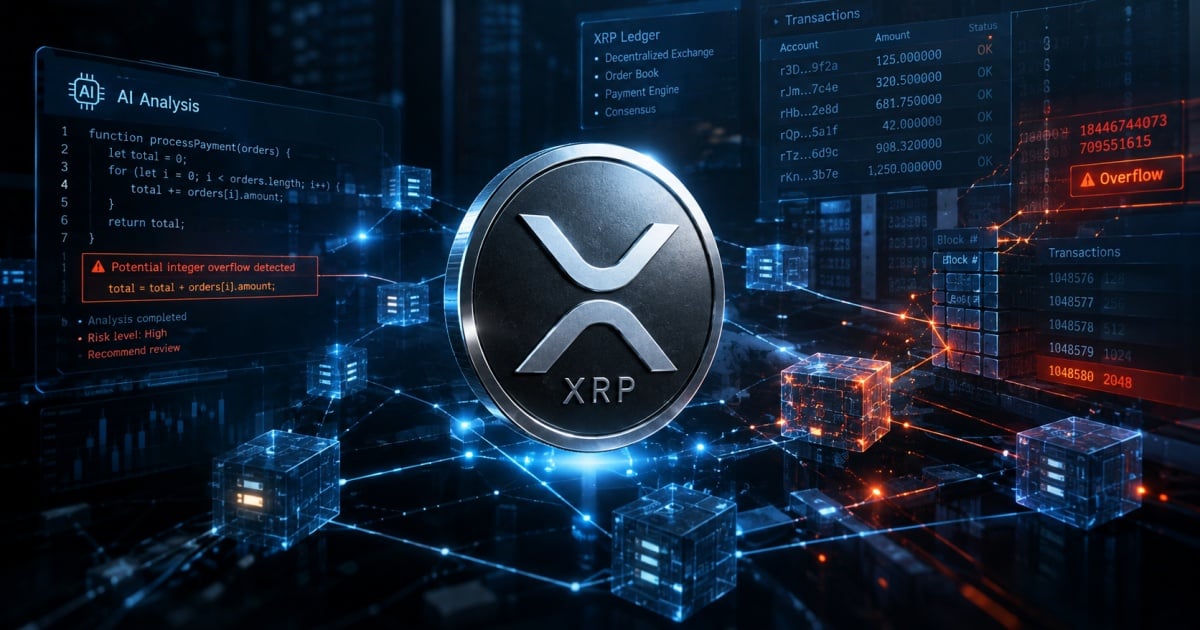
An integer overflow vulnerability that could have bypassed the XRP Ledger’s fixed-supply rule was identified by Veria Labs’ AI security agent while analyzing XRPL code. The agent linked a numerical overflow in the payment engine to a separate overflow in the supply-validation mechanism. Researchers then validated the attack path in a test environment, showing that a single transaction could theoretically create roughly 18.45 trillion XRP. There is no evidence the flaw was ever exploited on the public mainnet, and the relevant team mitigated the risk through an emergency software upgrade.
Why two small bugs became one big problem
The striking part of this episode is not the headline number, but the architecture it exposes. XRPL’s supply invariant is not enforced by a single check; it relies on multiple layers of code agreeing with each other. When two ostensibly independent boundary checks fail in a compatible way, the system’s core economic rule can be challenged even though no single line of code looks catastrophic on its own.
This is a familiar pattern in complex software, but it carries unusual weight in blockchain systems, where the ledger itself is the source of truth for scarcity. In traditional finance, a settlement error can be reversed by a custodian or clearinghouse. In a decentralized ledger, an exploited supply rule can permanently alter the asset’s monetary properties.
The AI angle cuts both ways
Veria Labs’ AI agent found the flaw by connecting code paths that human auditors may have reviewed separately. That is a genuine advance: AI tools can scan vast codebases and surface non-obvious interactions at a speed and scale that manual review cannot match. But the same capability also lowers the cost of finding exploitable bugs, meaning defenders must assume adversaries are using similar tools.
- Defensive upside: AI-assisted review can catch cross-module bugs before deployment.
- Offensive risk: The same techniques can be pointed at live protocols by attackers.
- Structural lesson: Supply invariants need formal, end-to-end verification, not just local checks.
What the industry should take from this
The emergency upgrade reduced immediate risk, but the deeper issue is verification methodology. Blockchains that promise fixed supply, capped issuance, or hard-coded monetary policy should treat those properties as system-level invariants and test them with formal methods, fuzzing, and adversarial AI agents. The XRP episode is a reminder that in layered code, security is only as strong as the weakest combination of assumptions — and that AI is now part of both the attack surface and the defense.