Hardware Wallet Maker COLDCARD Flags Compromised X Post in Ongoing Phishing Campaign
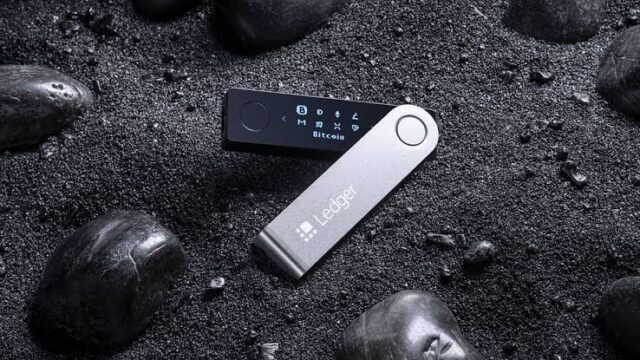
TREE NEWS reports: COLDCARD, the Bitcoin hardware wallet brand developed by Coinkite, has issued a public warning after a phishing message appeared on its official X account. The company said it found no matching login record associated with the suspicious post, suggesting the compromise may not have originated from a standard account access event. Separately, a security researcher who examined the fraudulent migration site said it was purpose-built to harvest wallet recovery phrases — the 12- or 24-word seeds that grant full control over a user’s bitcoin.
The incident is the latest in a long line of social-media account takeovers aimed at crypto users, but it carries a sharper edge: the attackers were not merely posting a fake giveaway or a malicious contract link. They were impersonating a wallet vendor and pushing a fake “migration” narrative, a tactic designed to convince holders that moving funds is not just safe but necessary.
Why Hardware Wallet Phishing Is Different
Hardware wallets exist precisely to keep private keys offline. That makes them a hard target for conventional malware — and an irresistible target for social engineering. If an attacker can convince a user to type a recovery phrase into a website, the device’s security model is bypassed entirely. No firmware exploit is required; the user simply hands over the keys.
The fake migration angle is particularly effective because it weaponizes a legitimate concern. Wallet users have grown accustomed to firmware updates, app migrations and chain upgrades, and phishing operators have learned to dress their traps in that same language. A spoofed post on a trusted account adds the final layer of credibility.
- Seed phrases are the single point of failure: Anyone who obtains them controls the funds, regardless of hardware.
- Brand accounts remain a soft target: Session hijacking, third-party tools and insider access all create exposure.
- Migration-themed scams are rising: Attackers exploit routine upgrade cycles to manufacture urgency.
The Broader Trust Problem for Wallet Makers
For firms like COLDCARD, the reputational stakes are high. Hardware wallet vendors sell trust as much as they sell silicon. A single convincing phishing post can erode that trust, even when the company itself was not breached in a conventional sense. The disclosure that no matching login record was found raises uncomfortable questions about session tokens, delegated access and the security of social-media management tools that many crypto firms rely on.
The incident also underscores a structural asymmetry. Attackers only need one successful click. Defenders must secure every channel — email, X, Discord, Telegram, support desks — simultaneously. For an industry that markets self-custody as the answer to counterparty risk, the weakest link is increasingly the human interface around the keys.
What Comes Next
Expect wallet makers to tighten operational security around social accounts, including hardware-key enforcement, stricter third-party app permissions and faster takedown coordination with platform providers. Users should treat any unsolicited instruction to “migrate” funds as hostile by default, and should verify announcements through multiple independent channels before acting.
The deeper lesson is that as crypto infrastructure matures, the attack surface shifts from code to communication. The most sophisticated cryptography in the world offers little protection against a convincing post on a trusted account and a user willing to type 24 words into the wrong box.