Recruitment as an Attack Vector
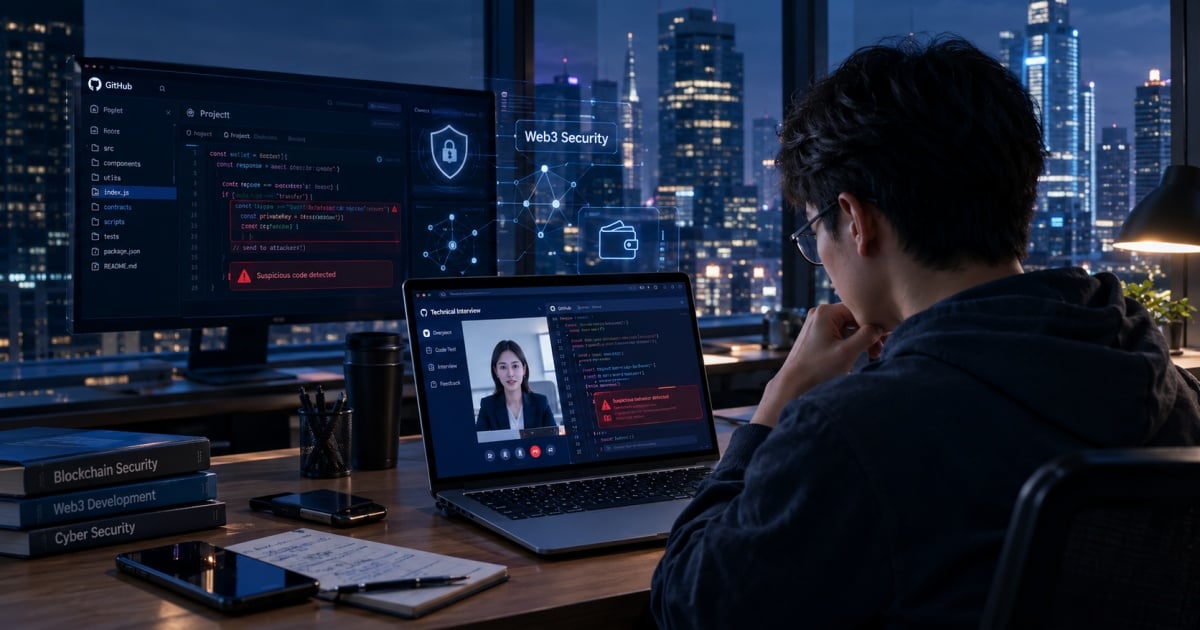
What looks like a routine job offer can now be the opening move in a sophisticated cyberattack. Japanese police, working alongside authorities in the United States, Australia, and Germany, have disclosed that a North Korea-backed threat group known as WaterPlum has spent years using fake recruitment processes to infiltrate global IT, AI, crypto, and NFT companies. The campaign has infected at least 30,000 devices across more than 100 countries, compromised roughly 7,000 crypto wallets, and moved an estimated ¥1.7 billion in digital assets.
Why Web3 Is the Prime Target
Unlike traditional finance, Web3 firms operate with a unique combination of high-value assets and relatively thin security infrastructure. Startups often lack dedicated security teams, and developers routinely execute code from unknown repositories as part of technical interviews. The attack chain is deceptively simple: a convincing recruiter contacts a target, shares a GitHub repository or coding test that contains malware, then follows up with a video interview that installs further payloads. Because the victim is an engineer with privileged access, a single successful compromise can cascade into wallet drains, private key theft, and protocol-level exploits.
The Industry Implications
- Trust is the weakest link: Recruitment pipelines are now a confirmed attack surface, yet most firms treat them as purely HR functions.
- Wallet hygiene is failing: The theft of 7,000 wallet credentials suggests that hot wallets and developer machines remain dangerously exposed.
- State actors are profiting: The scale of the operation — 100+ countries, tens of thousands of devices — indicates nation-state resources behind what is often dismissed as cybercrime.
The convergence of geopolitics and crypto is not theoretical. North Korea has long been accused of using stolen digital assets to fund state programs, and the WaterPlum disclosures give that narrative concrete evidence.
What Comes Next
Expect Web3 firms to overhaul hiring security: isolated environments for coding tests, verified recruiter identities, and mandatory hardware wallet usage for engineers. Regulators may also push for mandatory disclosure of security incidents tied to hiring processes. For now, the message is clear — in Web3, the next exploit may arrive disguised as a job offer.