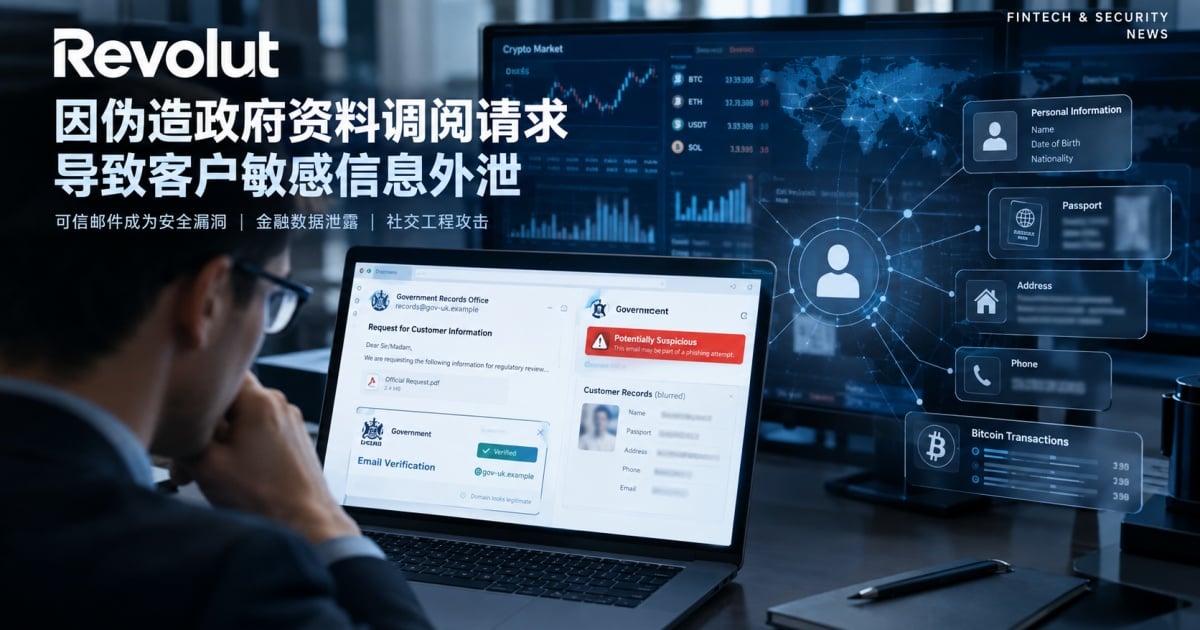
Revolut Breach Exposes KYC Weakness: When Fake Subpoenas Steal Crypto Data
Revolut has confirmed that attackers obtained customer data not by hacking its core infrastructure, but by exploiting a compromised government email domain to send forged law enforcement data requests. Internal teams, believing the subpoenas were legitimate, voluntarily handed over customer records. This is a stark reminder that the weakest link in financial security is often human trust in official-looking communication.
What Was Taken — and Why It Matters for Crypto
The exposed data reportedly includes names, addresses, passport details, and potentially complete Bitcoin transaction histories. For crypto users, this is far more dangerous than a typical privacy leak. When KYC identity data is bundled with on-chain activity, attackers gain a complete map linking real-world identities to digital asset holdings. That data can be used for targeted phishing, physical extortion, or sophisticated social engineering attacks against high-net-worth individuals.
The Rise of Social Engineering in Crypto
This incident is part of a broader trend. Attackers are increasingly bypassing technical defenses by manipulating people. In crypto, similar tactics have been used to compromise exchange support staff, trick wallet providers into revealing seed phrases, and impersonate regulators to pressure compliance teams. The Revolut case shows that even regulated financial institutions with robust cybersecurity can be defeated by a well-crafted email from a trusted domain.
Regulatory and Industry Implications
- Verification protocols must evolve: Financial institutions need multi-factor authentication for law enforcement requests, including out-of-band verification with the requesting agency.
- Data minimization is critical: Firms should collect only what is strictly necessary and store it in segmented, access-controlled environments.
- Crypto users need new defenses: Linking KYC to on-chain activity creates permanent risk. Privacy-preserving technologies and decentralized identity solutions may become essential.
Forward-Looking Perspective
As crypto adoption grows, the intersection of traditional finance compliance and digital asset transparency will only intensify. Regulators will likely push for stricter data handling standards, but the industry must also innovate. Zero-knowledge proofs, decentralized identifiers, and privacy-preserving KYC could reduce the blast radius of future breaches. Until then, every crypto user should assume that their identity data is a target — and act accordingly.