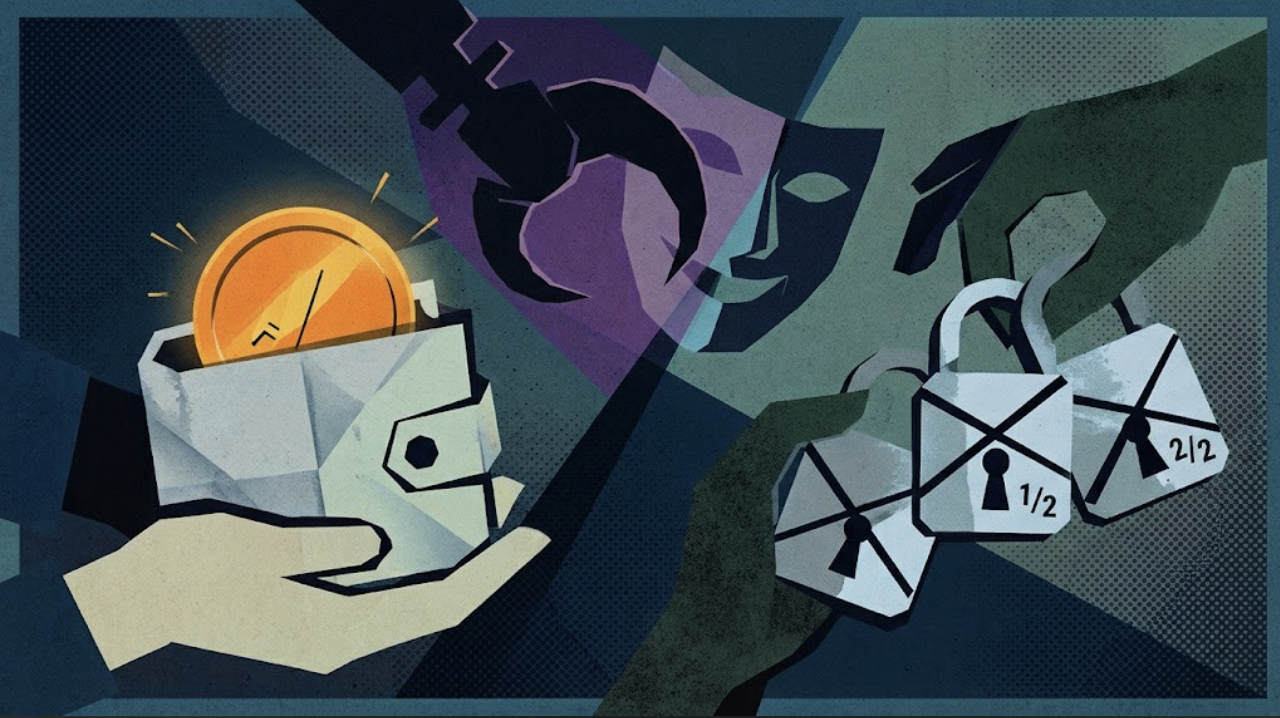
Your Coins Are Still There, But Someone Turned Your Wallet Into a Multisig: Theft or Fraud?
A troubling new pattern in crypto crime is forcing courts and investigators to confront an old legal question in a new technological context: when a attacker gains control of a wallet and changes its permissions to require multiple signatures—without moving any assets—has a theft occurred, or is it fraud? The distinction matters enormously for criminal liability, asset recovery, and the future of self-custody.
The mechanics of a permission hijack
In a typical case, an attacker compromises a user’s private key or seed phrase, then uses that access not to drain funds but to alter the wallet’s smart contract permissions or multisignature configuration. The original owner can still see the balance on-chain, but can no longer initiate transactions alone. The attacker effectively becomes a co-signer or gatekeeper, demanding payment to restore control.
This differs from a conventional hack because the assets remain in the same address. There is no direct transfer, no swap, no bridge. Legally, theft typically requires the unlawful taking of property with intent to permanently deprive. Fraud, by contrast, involves deception to obtain property or induce action. When the attacker uses social engineering to obtain the key, then locks the wallet, prosecutors may argue fraud. When the attacker exploits a smart contract vulnerability to change permissions without the owner’s knowledge, theft or unauthorized access claims may be stronger.
Why the legal gray zone matters
For victims, the practical problem is immediate: they cannot move their assets, but police may hesitate to act because no loss has been recorded on-chain. Exchanges and blockchain analytics firms are increasingly asked to trace permission changes, but few jurisdictions have clear statutes covering “wallet control hijacking” as a distinct offense. Insurance policies often exclude such events, and decentralized protocols have limited recourse mechanisms.
The ambiguity also creates a perverse incentive for attackers: by leaving funds in place, they may avoid triggering automated theft-detection systems and law enforcement thresholds that rely on asset movement. Some attackers use this window to negotiate ransoms, effectively monetizing control rather than possession.
Industry implications and forward outlook
Wallet developers are responding with better permission management, transaction simulation, and social recovery features. But the deeper issue is legal. As more value moves on-chain, courts will need to define whether control over a wallet constitutes a property interest separate from the assets it holds. Clearer rules would help victims, insurers, and investigators.
Until then, users should treat key management as a security perimeter, not just a password. Multisig setups, hardware wallets, and permission monitoring are no longer optional for high-value accounts. The next wave of crypto litigation may not be about stolen coins, but about stolen control—and the law is not yet ready.